Every blueprint ships with source code, sample data, and step-by-step instructions — ready to run on your Cloudera Platform
-
Blueprint Card
Overview
CDP Agent Gateway is agent governance for Cloudera Data Platform. Cursor, Claude, and other MCP hosts can run Spark, Hive, and Impala without learning cluster topology and without a parallel credential path. Apache APISIX terminates agent HTTP, validates Knox-issued RS256 JWTs, and forwards the same bearer into Knox Livy for Spark 3. Agents use MCP for Spark. Operators can GET Livy for tests and stage job files with WebHDFS. Knox Trusted Proxy and Apache Ranger remain the authorization source of truth. Operator quotas, burst caps, and audit join record which agent product and which Knox user called which tool.
Hive is inventoried and agents use read-only MCP for Hive. Impala uses read-only MCP. Direct Hive and Impala endpoints are not agent routes. Ozone and NiFi stay unpublished. Cloudera value is unchanged identity and data policy: agents do not get a parallel credential path into the lakehouse.
CDP Agent Gateway governs AI-agent access to Spark, Hive and Impala, eliminating topology knowledge and separate credentials.
Demo
A recorded Reprise walkthrough is not published yet. The current path is the local Docker stack in Quickstart: mock Knox, APISIX, Spark MCP, read-only Hive MCP, read-only Impala MCP, and the operator admin UI. Pytest covers missing bearer, alg=none, expired tokens, subject forwarding, and MCP tool list. The minted JWT is for the lab only; live Knox uses a real Knox token set through the gateway CLI. The admin console is for operators, not MCP hosts, and a full walkthrough is in the admin docs. Third-party agents are demonstrated with the Jupyter notebooks in the examples folder, not the operator CLI. The third-party agent notebook is a scripted MCP host (the same POST JSON-RPC a Cursor or Claude host would send). The LangGraph notebook shows LangGraph: a ReAct agent bound to the same Spark, Hive, and Impala tools. Both present a Knox JWT and never call cluster APIs directly. On a live cluster that notebook path is what produces the Spark History, Data Catalog, and operator activity evidence: the Spark submit batch tool writes a count_to_10 table as the Knox subject, then Hive MCP selects it. Watch the demo
Key Features
Agent governance — Knox identity, Ranger authorization, MCP allowlists, per-user quotas, and audit join. Ranger stays authoritative, and the gateway does not impersonate a different user than the token subject.
Knox JWT at the agent edge — no second token format and no APISIX-minted user credentials. An agent key names the agent product, and the Knox JWT subject is the CDP user. RFC 9728 protected resource metadata lets MCP hosts discover how to authenticate.
Spark, Hive, and Impala MCP — Spark supports list, get, log, and submit. Hive and Impala are read-only list, describe, and select (no SELECT *, limit 50), and their direct endpoints are never exposed to agents.
Operator controls — an admin UI shows UTC-day usage, quotas vs burst limits, and audit join, with an MCP burst cap per Knox user (default 60/minute). The CLI manages JDBC inventory and points the same local stack at a live Knox cluster.
Third-party agent notebooks — demos of a scripted MCP host and a LangGraph ReAct agent running against the Spark, Hive, and Impala tools.
Use Case
Enterprises need to govern coding and analytics agents that submit Spark jobs and query Hive or Impala on CDP. They cannot publish Livy, HiveServer2, or Impala to those tools, and they cannot mint a second identity plane. This blueprint gives one agent-facing address that allows Spark MCP plus read-only Hive and Impala MCP, binds each call to a Knox user, keeps Ranger in charge of data access, and gives operators quotas plus audit join — without replacing the CDP perimeter.
Architecture
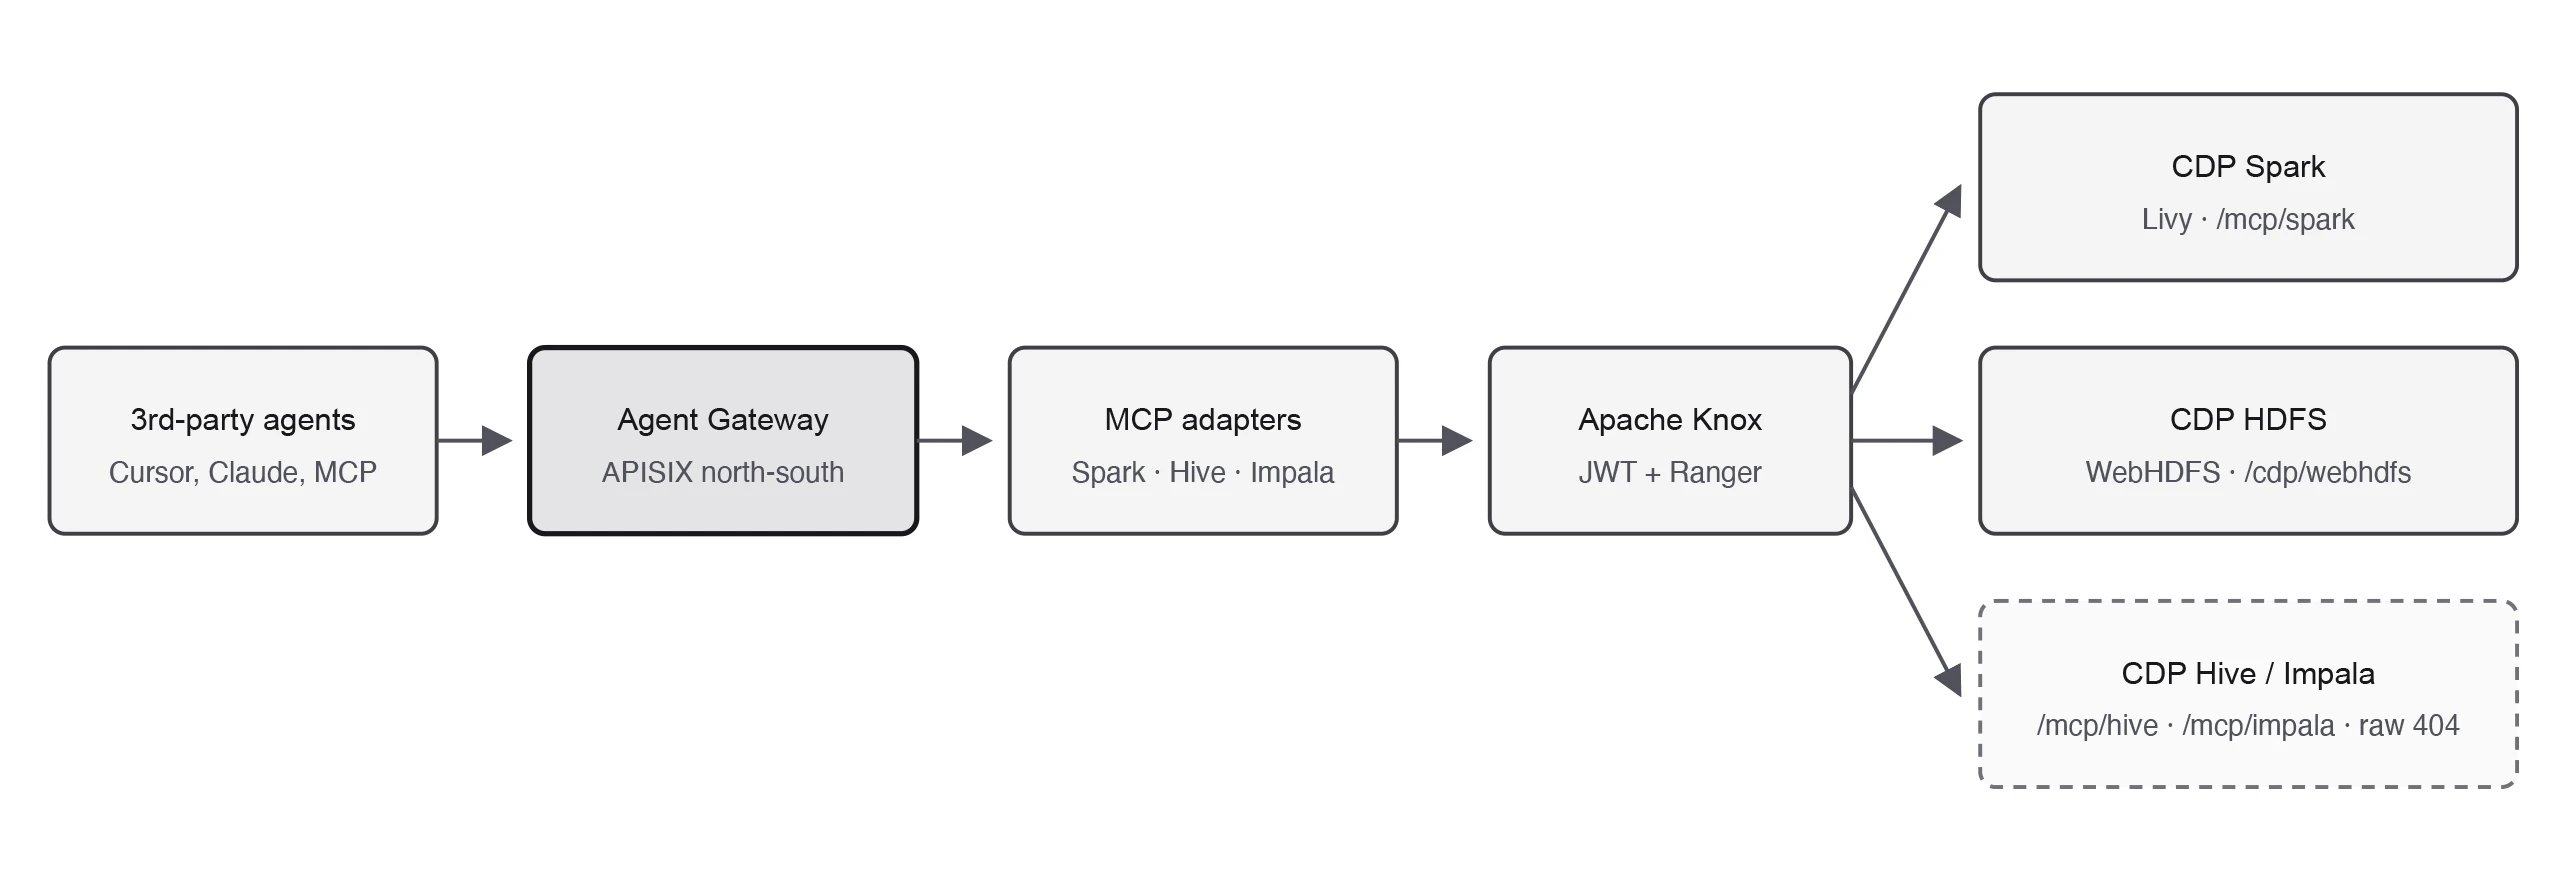
CDP Agent Gateway places an Apache APISIX gateway in front of Cloudera Data Platform, and that gateway checks the Knox-issued token that every agent request must carry. Approved requests go to dedicated Spark, Hive, and Impala adapters, which pass the user's original token through Apache Knox to the underlying cluster services. Knox remains the only component with cluster credentials, Apache Ranger decides what each user is allowed to do, and the gateway adds rate limits, daily quotas, and an audit trail of which user and agent made each call.
Your form submission has failed.
This may have been caused by one of the following:
- Your request timed out
- A plugin/browser extension blocked the submission. If you have an ad blocking plugin please disable it and close this message to reload the page.